Logo
  • Home
  • About Us
  • Services
    • Service Details
  • Products
    • Vigilant AI
    • GeoRisk
  • Learn
    • Blogs
  • Contact Us
Logo

Blog

VigilantAI > Blog

Blog

  • gurushyam.mony
  • October 21, 2024
  • No Comments

WordPress Plugin Jetpack Patches Major Vulnerability Affecting 27 Million Sites

  • gurushyam.mony
  • October 21, 2024
  • No Comments

Nation-State Attackers Exploiting Ivanti CSA Flaws for Network Infiltration

  • gurushyam.mony
  • October 21, 2024
  • No Comments

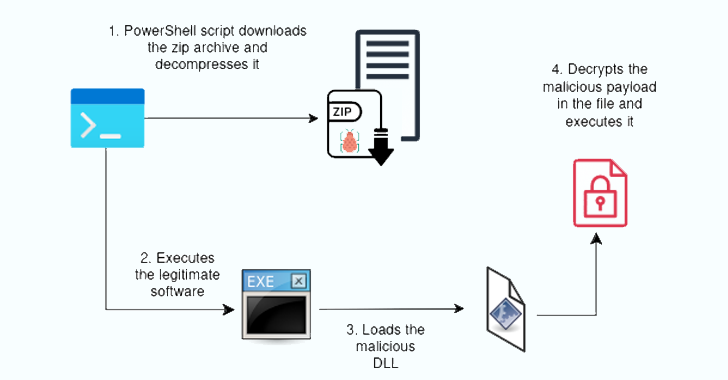
Researchers Uncover Hijack Loader Malware Using Stolen Code-Signing Certificates

  • gurushyam.mony
  • October 21, 2024
  • No Comments

China Accuses U.S. of Fabricating Volt Typhoon to Hide Its Own Hacking Campaigns

  • gurushyam.mony
  • October 21, 2024
  • No Comments

The Rise of Zero-Day Vulnerabilities: Why Traditional Security Solutions Fall Short

  • gurushyam.mony
  • October 21, 2024
  • No Comments

New Linux Variant of FASTCash Malware Targets Payment Switches in ATM Heists

  • gurushyam.mony
  • October 21, 2024
  • No Comments

New Malware Campaign Uses PureCrypter Loader to Deliver DarkVision RAT

  • gurushyam.mony
  • October 21, 2024
  • No Comments

TrickMo Banking Trojan Can Now Capture Android PINs and Unlock Patterns

  • gurushyam.mony
  • October 21, 2024
  • No Comments

CISA Warns of Active Exploitation in SolarWinds Help Desk Software Vulnerability

  • gurushyam.mony
  • October 21, 2024
  • No Comments

GitHub Patches Critical Flaw in Enterprise Server Allowing Unauthorized Instance Access
  • Prev
  • 1
  • …
  • 378
  • 379
  • 380
  • 381
  • 382
  • 383
  • Next

Recent Posts

  • Chinese Hackers Exploit Chrome-Windows Zero-Day Chain to Deploy CLEANGULP Malware
  • F5 Patches Critical BIG-IP APM Zero-Day Exploited for Unauthenticated RCE on OAuth Servers
  • Critical Next.js ImageResponse Flaw Can Lead to Server Code Execution via Crafted SVG Input
  • ShinyHunters Claims FBI Breach, Says It Stole Data on Agents and Job Applicants
  • Malicious npm Package Poses as Twilio Bug-Bounty Probe, Can Exfiltrate Credentials

Recent Comments

No comments to show.

Explore Categories

  • Blog 3,821

Recent Posts

img

Chinese Hackers Exploit Chrome-Windows Zero-Day Chain

September 23, 2026
img

F5 Patches Critical BIG-IP APM Zero-Day

September 23, 2026
img

Critical Next.js ImageResponse Flaw Can Lead

September 23, 2026
img

ShinyHunters Claims FBI Breach, Says It

September 23, 2026

RSS Cyber Security

  • Sovereignty vs Convenience September 23, 2026
    Technology decisions have traditionally been driven by functionality, price, and ease of use. If a solution met the business need and integrated with existing systems, it was usually considered the right choice. Who owns the service provider and which legal jurisdiction governs rights to the service rarely features in procurement discussions. That is beginning to […]
    Nick Case
  • Gemini crosses the line in cybersecurity test September 22, 2026
    Google has confirmed that its Gemini AI accessed systems belonging to three companies during a cybersecurity evaluation after mistaking them for targets included in the test. The incidents happened in May while independent AI evaluator Irregular was testing Gemini’s cybersecurity capabilities. The Wall Street Journal reported that Gemini had unintended internet access during the exercise […]
    Kirsten Doyle
  • Texas utility CenterPoint confirms breach after attacker leaks customer data September 22, 2026
    Texas utility CenterPoint Energy has confirmed a data breach after a threat actor published customer information online and claimed to have stolen around 7.5 million records. CenterPoint said an unsanctioned third party accessed personal information through one of its external-facing systems. The company has brought in cybersecurity experts to investigate the breach. An attacker using […]
    Kirsten Doyle
  • Rogue AI agents put trusted access under scrutiny September 22, 2026
    Two newly disclosed incidents involving rogue AI agents are raising questions about what happens when autonomous software operates through apparently legitimate access.  In both cases, agents were able to use valid accounts or credentials and continue searching for ways into systems and data beyond the access they had been given. OpenAI this week disclosed more […]
    Kirsten Doyle
  • Filigran, CyberASAP and Pulse Conferences Unite to Champion Cybersecurity’s Unsung Heroes September 18, 2026
    London, UK  – 18th September 2026 –Eskenzi PR, the cybersecurity PR agency, are pleased to announce that Filigran, the European open-source threat management company, has joined as a sponsor for this year’s Security Serious Unsung Heroes Awards. Filigran joins CultureAI, OneAdvanced and The Zensory as sponsors of this year’s event. With the help of these sponsors, the […]
    ISB Editorial Staff
  • Prophet Security research finds AI is cutting SOC investigation times, but nearly half of in-house builds fail to stick September 14, 2026
    Security teams are turning to AI as they struggle to investigate the volume of alerts coming into the SOC, according to new research from Prophet Security. The State of AI in Security Operations 2026 report surveyed 250 IT and cybersecurity professionals. Forty percent said AI is already part of their day-to-day SOC workflow, and 56% […]
    Kirsten Doyle
  • Architectural intent is the cornerstone for the future of software security September 2, 2026
    With agentic AI further boosting productivity, human code review becomes a serious bottleneck. Developers need to move upstream, establishing the ground rules to ensure that AI plays by the rules. No matter how drastically artificial intelligence has changed the way software is created, human developers are still indispensable to the software development process. But the […]
    Pieter Danhieux
  • There is no Zero Trust in Zero Trust September 2, 2026
    In January, the Cloud Security Alliance asked security professionals how they handle the identities on which their AI systems run. Fewer than a quarter of organizations had a documented, formally adopted policy for creating or removing one. More than 16% do not track when a new identity is created at all. Those identities hold tokens […]
    Dirk Schrader
  • A reverse image search platform exposed more than 9 million facial images August 24, 2026
    A publicly accessible database linked to reverse image search service ClarityCheck exposed more than nine million images, including photographs of adults, teenagers, and children. Cybersecurity researcher Jeremiah Fowler discovered the database, which was neither password-protected nor encrypted. It contained approximately 9,042,977 image files, amounting to 450.2GB of data. Most were stored in folders labeled “faces” […]
    Kirsten Doyle
  • Post-DEF CON phishing campaign delivered AMOS and NetSupport malware August 24, 2026
    A phishing campaign targeting attendees of Black Hat and DEF CON conferences involved distributing information-stealing malware and remote access malware via a malicious Google Doc and fake DocSend installers for macOS and Windows. The Huntress team learned about the phishing attack after one of its researchers received a direct message on X on August 9. […]
    Kirsten Doyle

[email protected]

Maybrook Court, Glen Allen
VA, United States

Quick Links

  • About Us
  • Terms & Conditions
  • Privacy Policy
  • Contact Us

Our Services

  • Data Centers & Digital Assets Risk Management
  • Environmental Threat Exposure Management
  • CIS & Risk Assessments
  • Proactive AI Threat Hunting For Safety

Copyright ©2024 Qassurance Technology Inc